Alba Dental Clinic
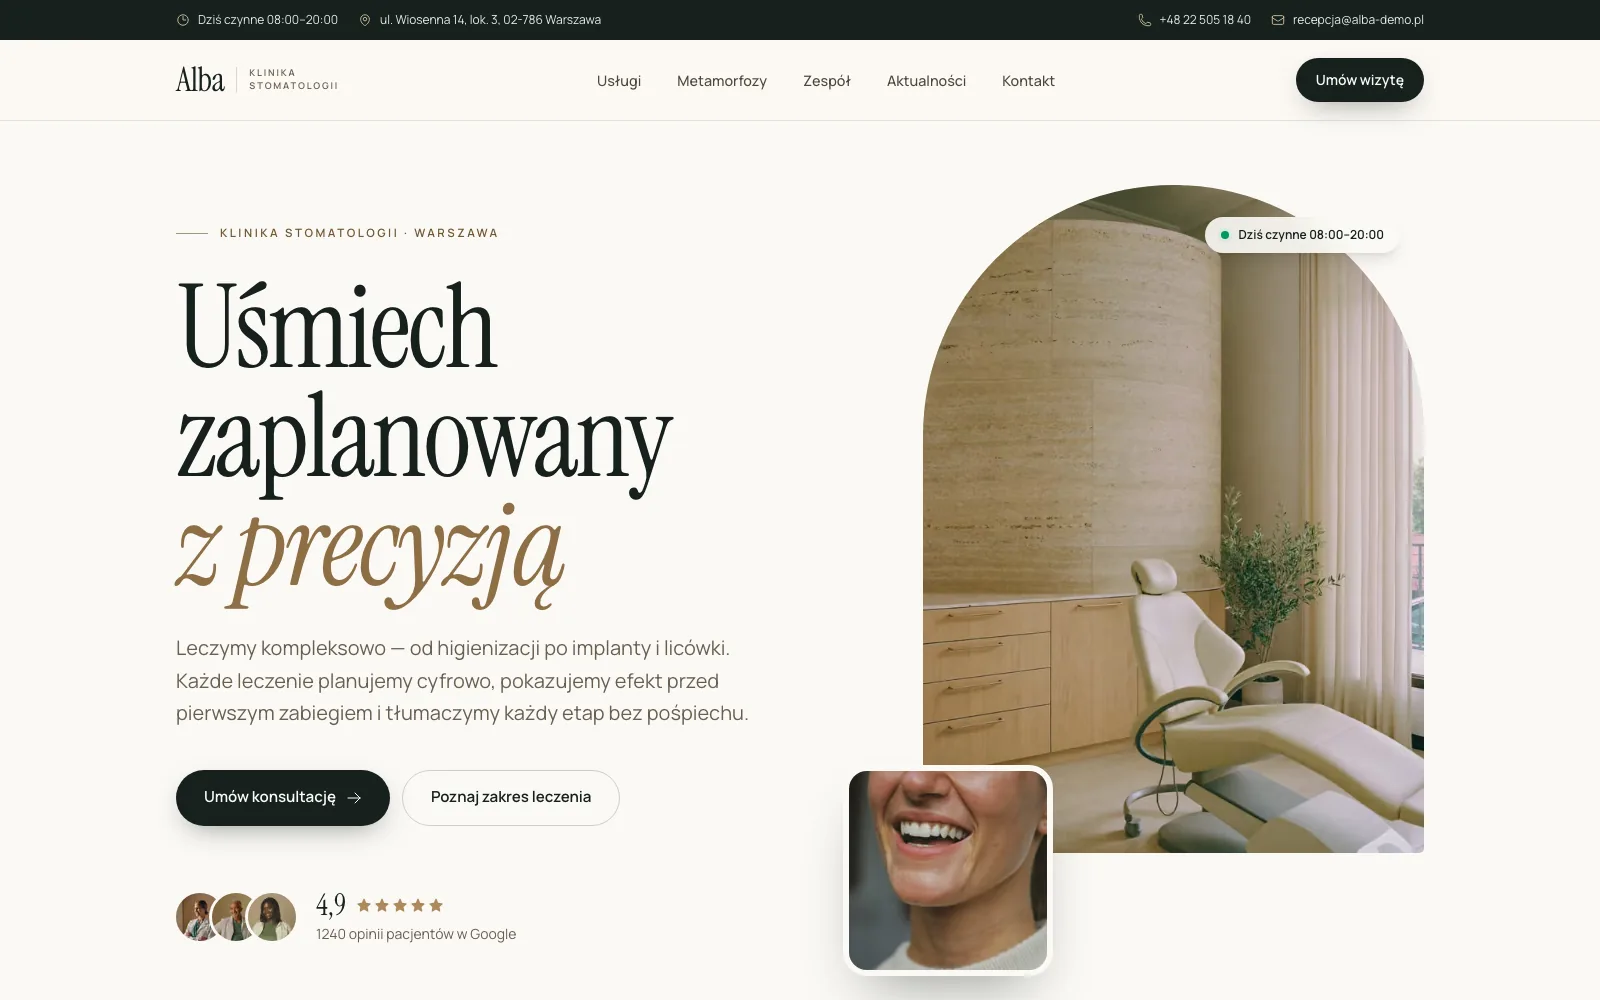
A premium dental clinic website with its own CMS, running in production on a hardened VPS — editable content, before/after gallery, online booking and patient data handled with GDPR in mind.
- Category
- Clinic website + CMS / Self-hosted
- Industry
- Healthcare / Dentistry
- Website
- alba.oksoftware.co
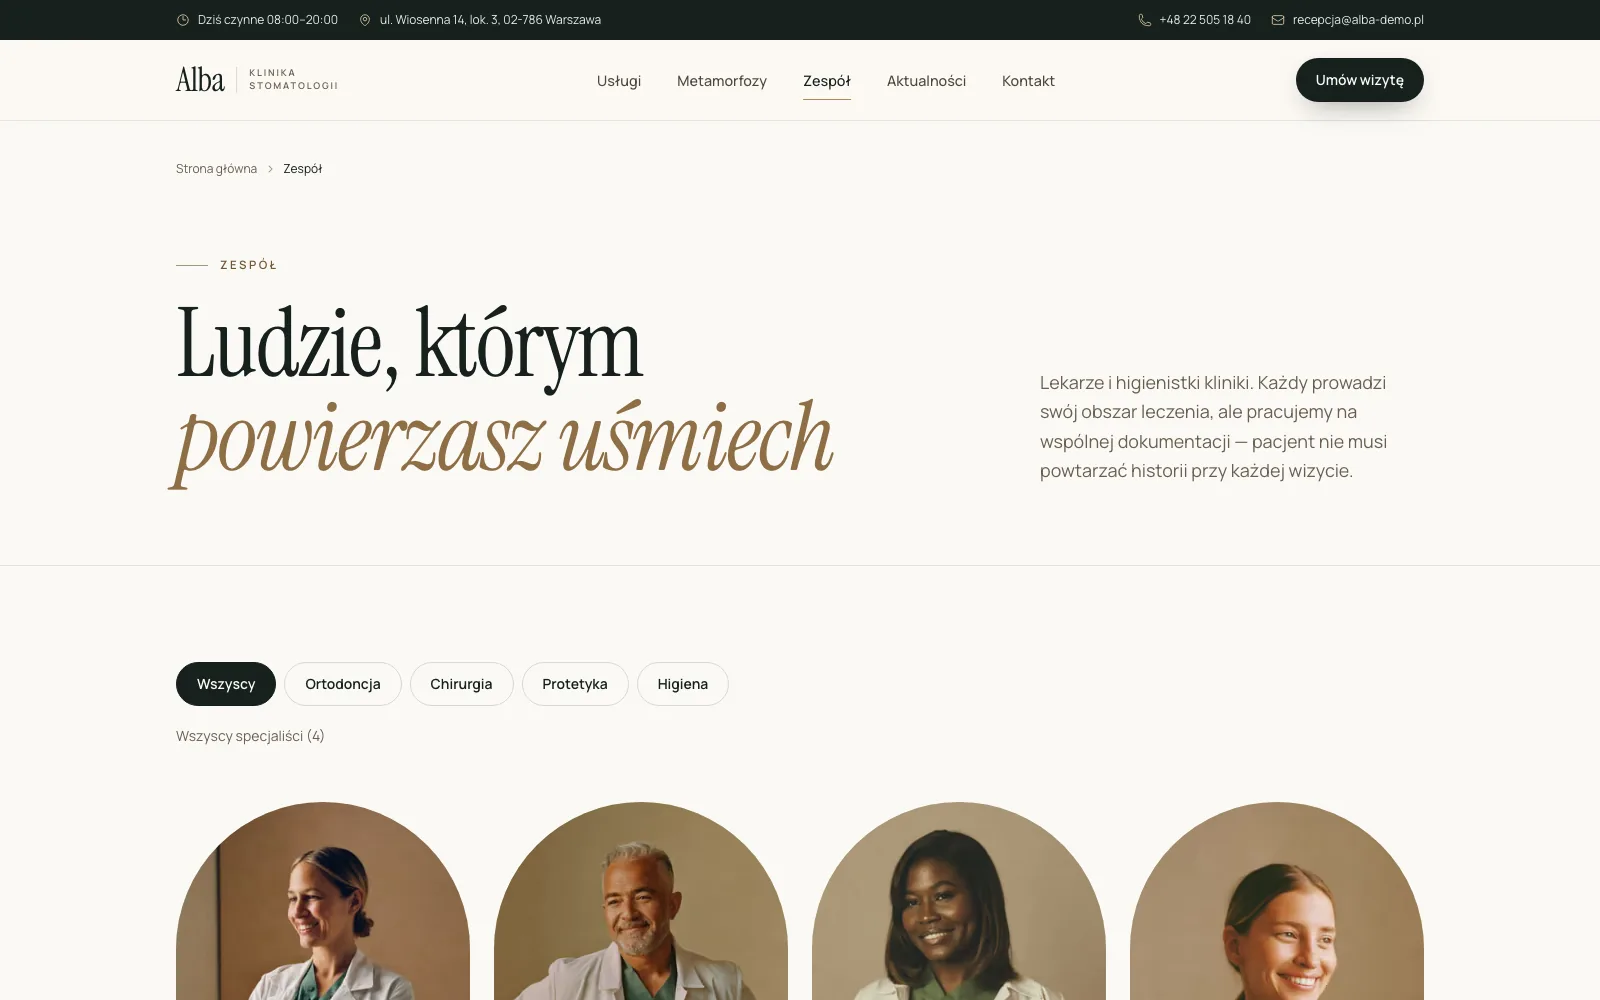
Alba is a complete, production-grade website for a dental clinic: a fast public site the clinic can edit on its own, an editorial panel, and infrastructure built from an empty server to a monitored, backed-up deployment. It is an internal reference project — the clinic and its data are fictional — built to show what a modern, secure clinic website should look like end to end.
The Challenge
Clinic websites are often slow, hard to update and careless with patient data: contact forms that copy health details into email inboxes, third-party widgets loaded before any consent, admin panels open to the whole internet. The goal was a site that looks premium, that staff can update without a developer, and that treats patient data seriously at every layer.
Our Approach
Next.js for the public site and Strapi as the editorial panel, both on PostgreSQL behind Caddy, all in Docker on a single VPS. Images are built in GitHub Actions and deployed by commit SHA, so every release is reproducible and can be rolled back with one command. Security is layered — network, server, HTTP, application and CMS — so that breaking one layer does not open the others.
What We Built
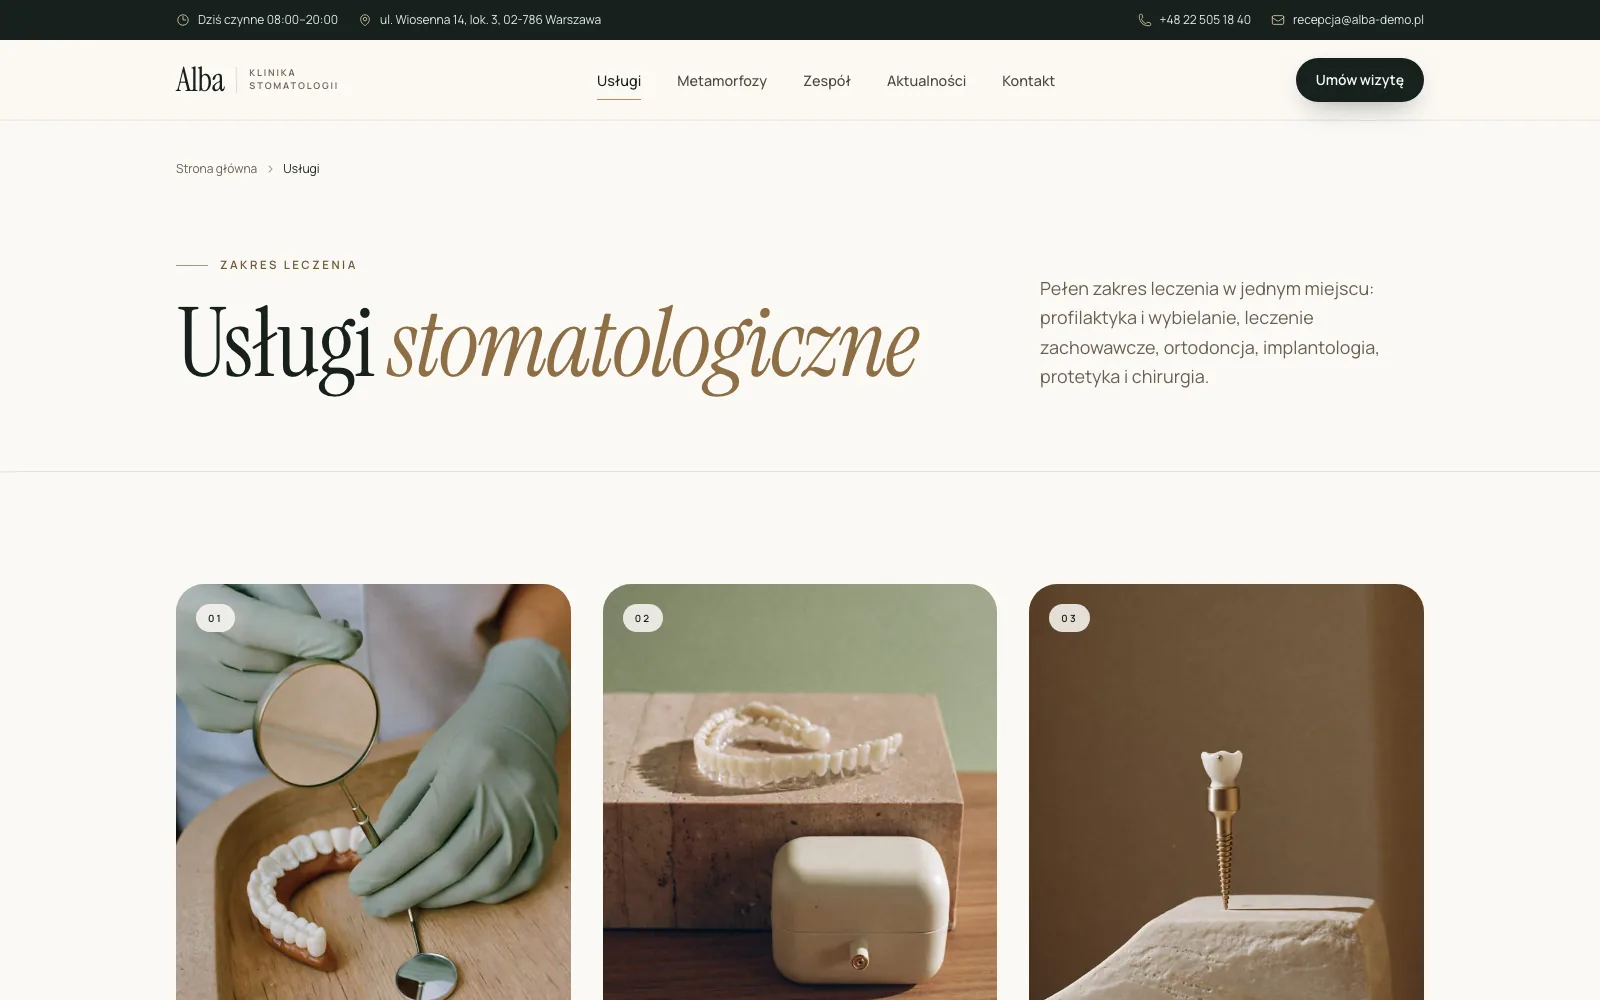
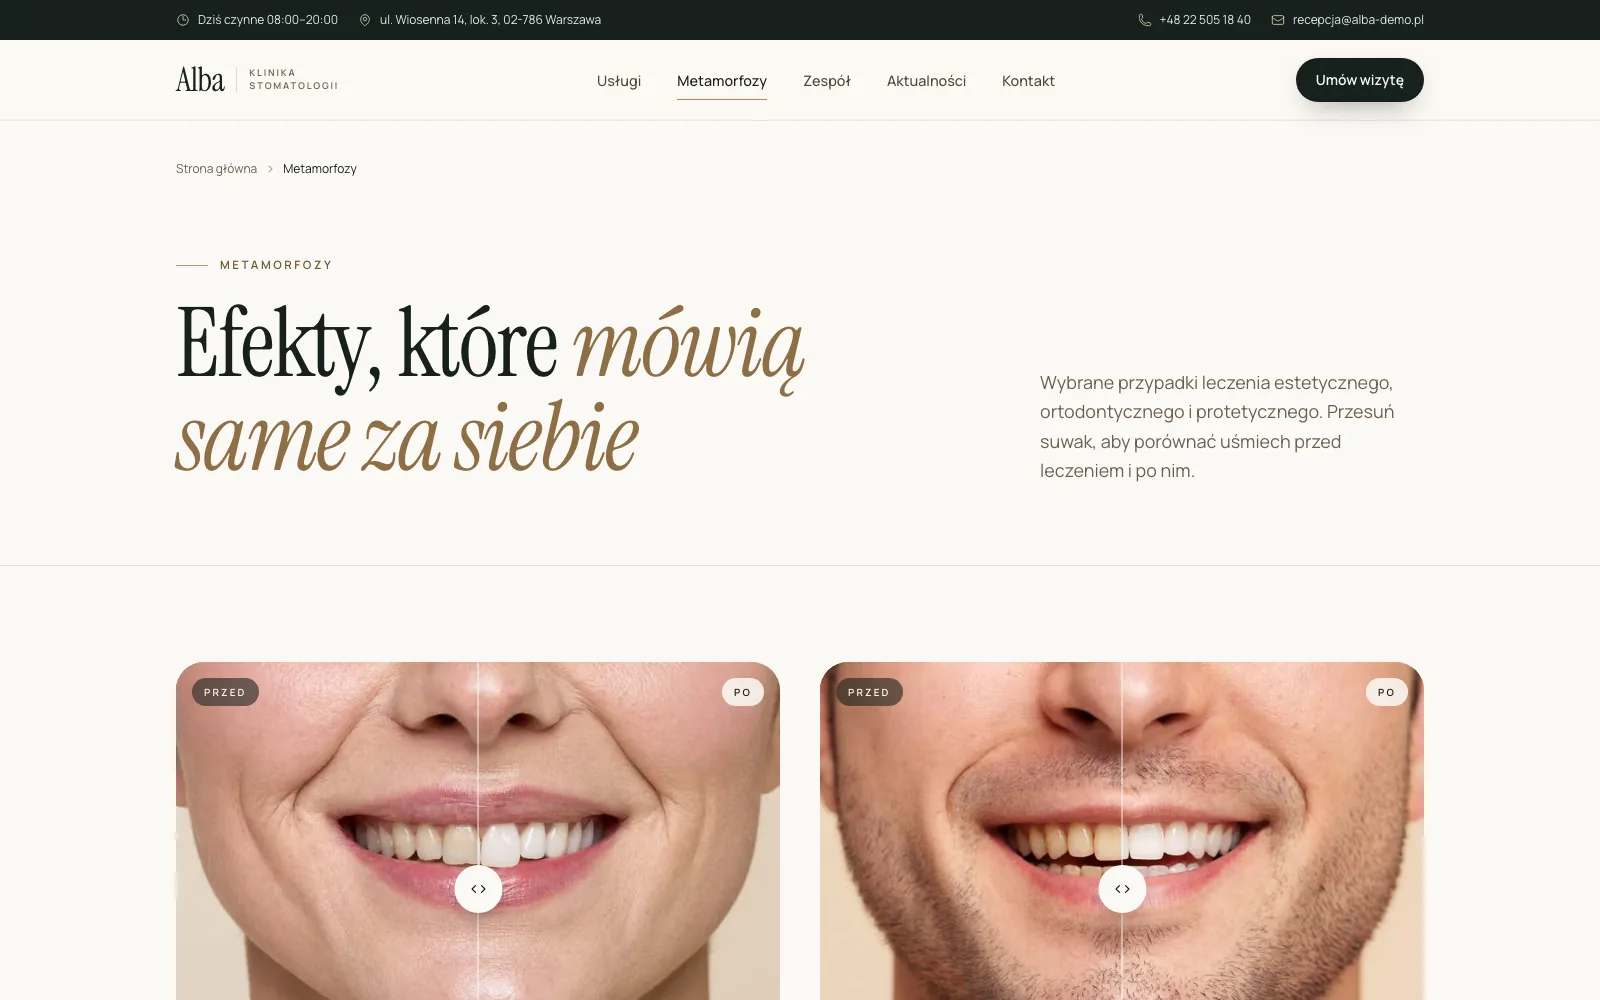
- Public site: services, before/after gallery with a comparison slider, team with specialty filter, news, patient reviews, contact
- Strapi CMS in Polish and English — staff edit services, team, news and gallery on their own
- Contact form stored only in the CMS (no copies in email or logs), with automatic deletion after the retention period
- Online booking embedded as an iframe from an allow-listed provider — no vendor scripts on the page
- Map loaded only after the visitor's consent, so no third party receives their IP address beforehand
- Content-Security-Policy with a per-request nonce, CSRF protection, rate limiting and a honeypot on the form
- Custom rich-text renderer — CMS content never reaches the page as raw HTML
- Read-only public API, CORS locked to a single origin, isolated database network
- Hardened server: firewall covering Docker traffic, fail2ban, key-only SSH, containers without root privileges
- Encrypted off-site backups with tested restore, uptime monitoring and server audit scripts
Results
- Running in production at alba.oksoftware.co
- Every release reproducible from a single commit and reversible in one step
- Patient enquiries never leave the clinic's own system
- Honest about scope: the clinic, staff, reviews and contact details are fictional demo content
Tech Stack
Next.js 16 (App Router), React 19, TypeScript, Tailwind CSS v4, Strapi 5, PostgreSQL 17, Caddy 2 with rate limiting, Docker Compose, GitHub Actions with GitHub Container Registry, restic backups, Debian VPS.
Want a system like this?
No salespeople — talk to a Lead Engineer about your process.